Summary
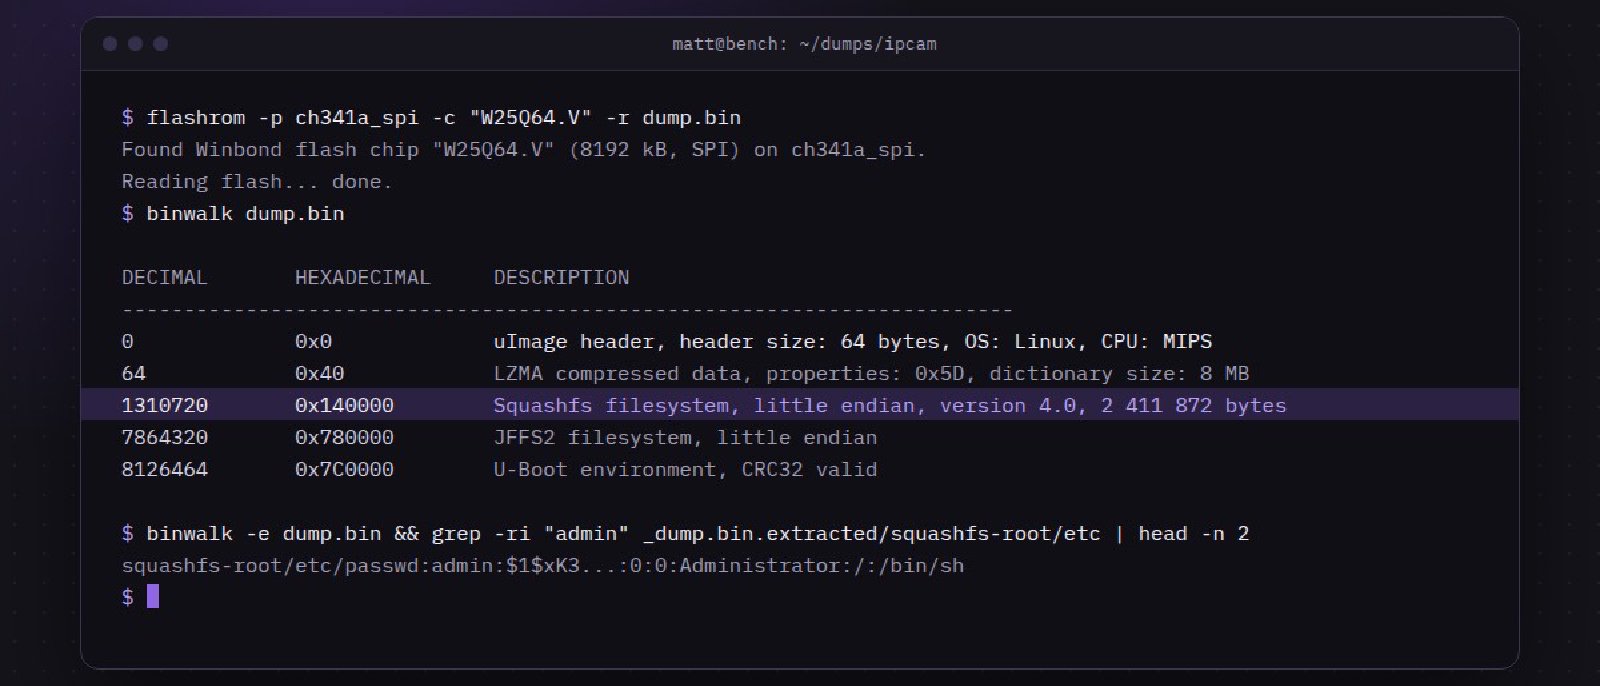
The vendor publishes no firmware images, so the only way in was the flash chip. Clipping onto the SOIC-8 package and reading it in-circuit gave a clean 8 MiB dump on the third attempt. Strings and a quick unpack exposed a default administrator password shared across the product line.
Background
Budget cameras are built from a small set of reference designs, which means one teardown often generalises across a dozen brands. This one uses a common SoC, a 25-series SPI flash and an unpopulated UART header next to the antenna.
Method
I identified the flash from its markings, powered the board from a bench supply at 3.3 V so the SoC stayed in reset, and read the chip over SPI. A logic analyser on the same pins let me confirm the clock speed and rule out contention with the SoC.
Findings
The image contains a SquashFS root filesystem and a U-Boot environment. The environment leaves the bootloader prompt reachable over the UART with no delay, and the web interface ships with a fixed administrator account.
Takeaways
Lock the bootloader, remove default credentials, and treat the flash chip as readable by anyone with a clip. For researchers: a logic analyser is worth its price the first time a dump comes back half corrupted.